Compliance Management
SOC 2, HIPAA and PCI DSS without the scramble. As a Secureframe partner, Red Key automates the security and compliance process for companies in New York City, Westchester, Connecticut, Los Angeles, Florida, and nationally.
Is a customer, investor or regulator asking for your SOC 2 report, HIPAA safeguards or PCI attestation?
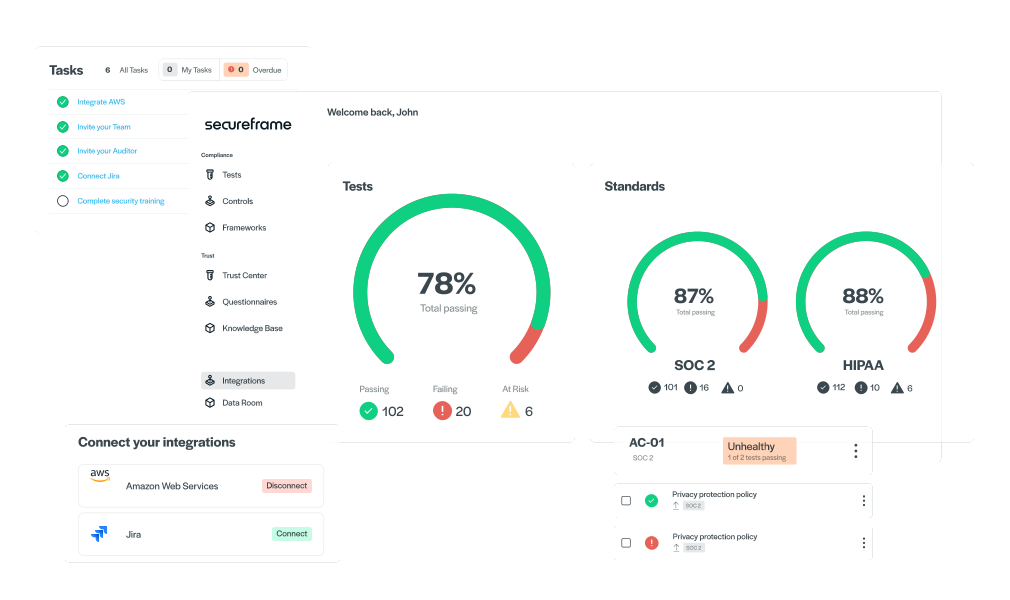
Red Key is a Secureframe partner. Secureframe connects to the tools you already run, tests your controls continuously and collects audit evidence automatically. Our team configures it, monitors it and does the remediation work, so compliance becomes something that runs in the background instead of a quarterly fire drill.
We choose the framework, define what is in scope and run a gap assessment against every control.
Secureframe connects to your cloud, identity, HR and device platforms. Evidence starts collecting on day one.
We close the gaps, roll out policies, train your team and manage vendor and risk reviews.
We coordinate the audit, then continuous monitoring keeps you compliant all year, not just at audit time.
 Microsoft 365
 Azure
 Defender
 Sentinel
 Teams
 AWS
 Google Workspace
 GitHub
 Azure DevOps
 CrowdStrike
 1Password
 Duo
 KnowBe4
 Snyk
 Checkr
 Slack
 Zoom
 Jira
 Asana
 Salesforce
Microsoft 365, Entra ID, Azure, Defender, AWS, Google Workspace, GitHub, your HR system and your device management platform. Secureframe pulls evidence from each of its 300+ integrations automatically, so nobody on your team is screenshotting settings the week before the audit. Because Red Key already manages most of these systems for our clients, the integration work is usually done in days.
We start with a scoping call and a gap assessment against the framework you need, then connect Secureframe to your cloud, identity, HR and device platforms so evidence collects itself. Our team remediates the gaps, writes the policies, trains your people and coordinates with the auditor. Once your report is issued, continuous monitoring keeps you compliant year after year.